Case Study: From HTML Injection to Credential Theft
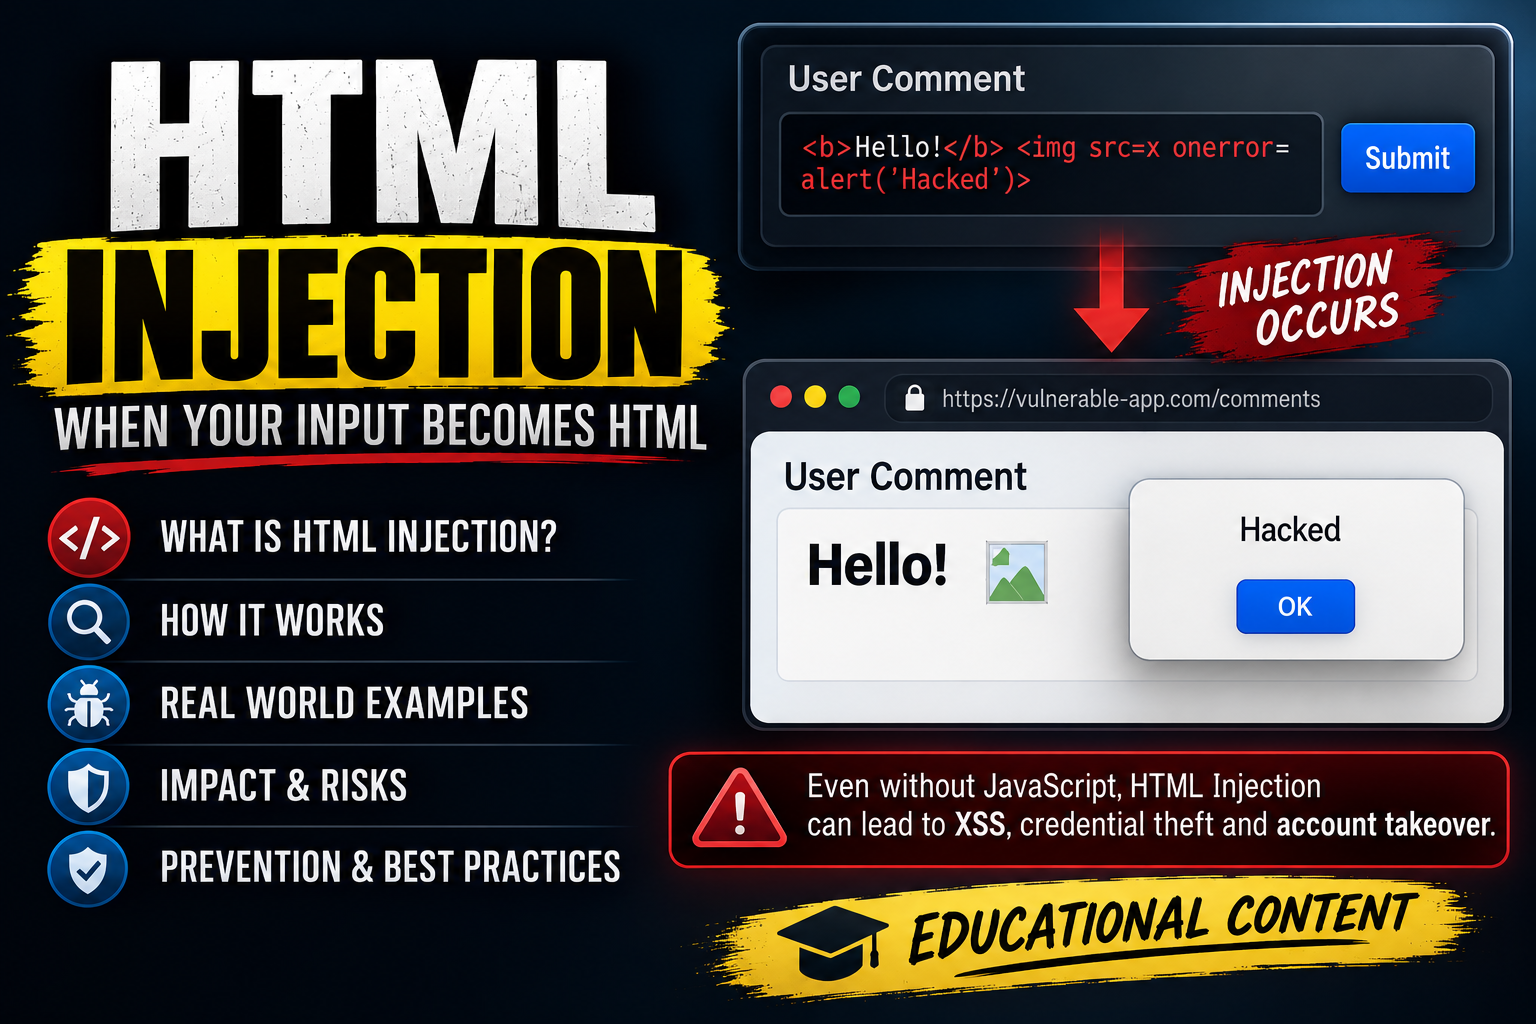
Examining how insufficient HTML sanitization enables credential phishing through attacker-controlled content Full video at https://youtu.be/XDD-hwdWJjY
Series
Exploring real-world vulnerability patterns through controlled lab reproductions, technical exploitation walkthroughs, root cause analysis, and practical remediation techniques.
Examining how insufficient HTML sanitization enables credential phishing through attacker-controlled content Full video at https://youtu.be/XDD-hwdWJjY
How weaknesses in OAuth account linking and authentication flows can allow attackers to compromise user accounts before legitimate registration. Full video at : https://youtu.be/tDXNoB5-_2o
How broken tenant isolation and missing authorization checks in backup restoration can allow attackers to access sensitive data belonging to other organizations. Full video at : https://youtu.be/AshvGLWsclw